10 min read
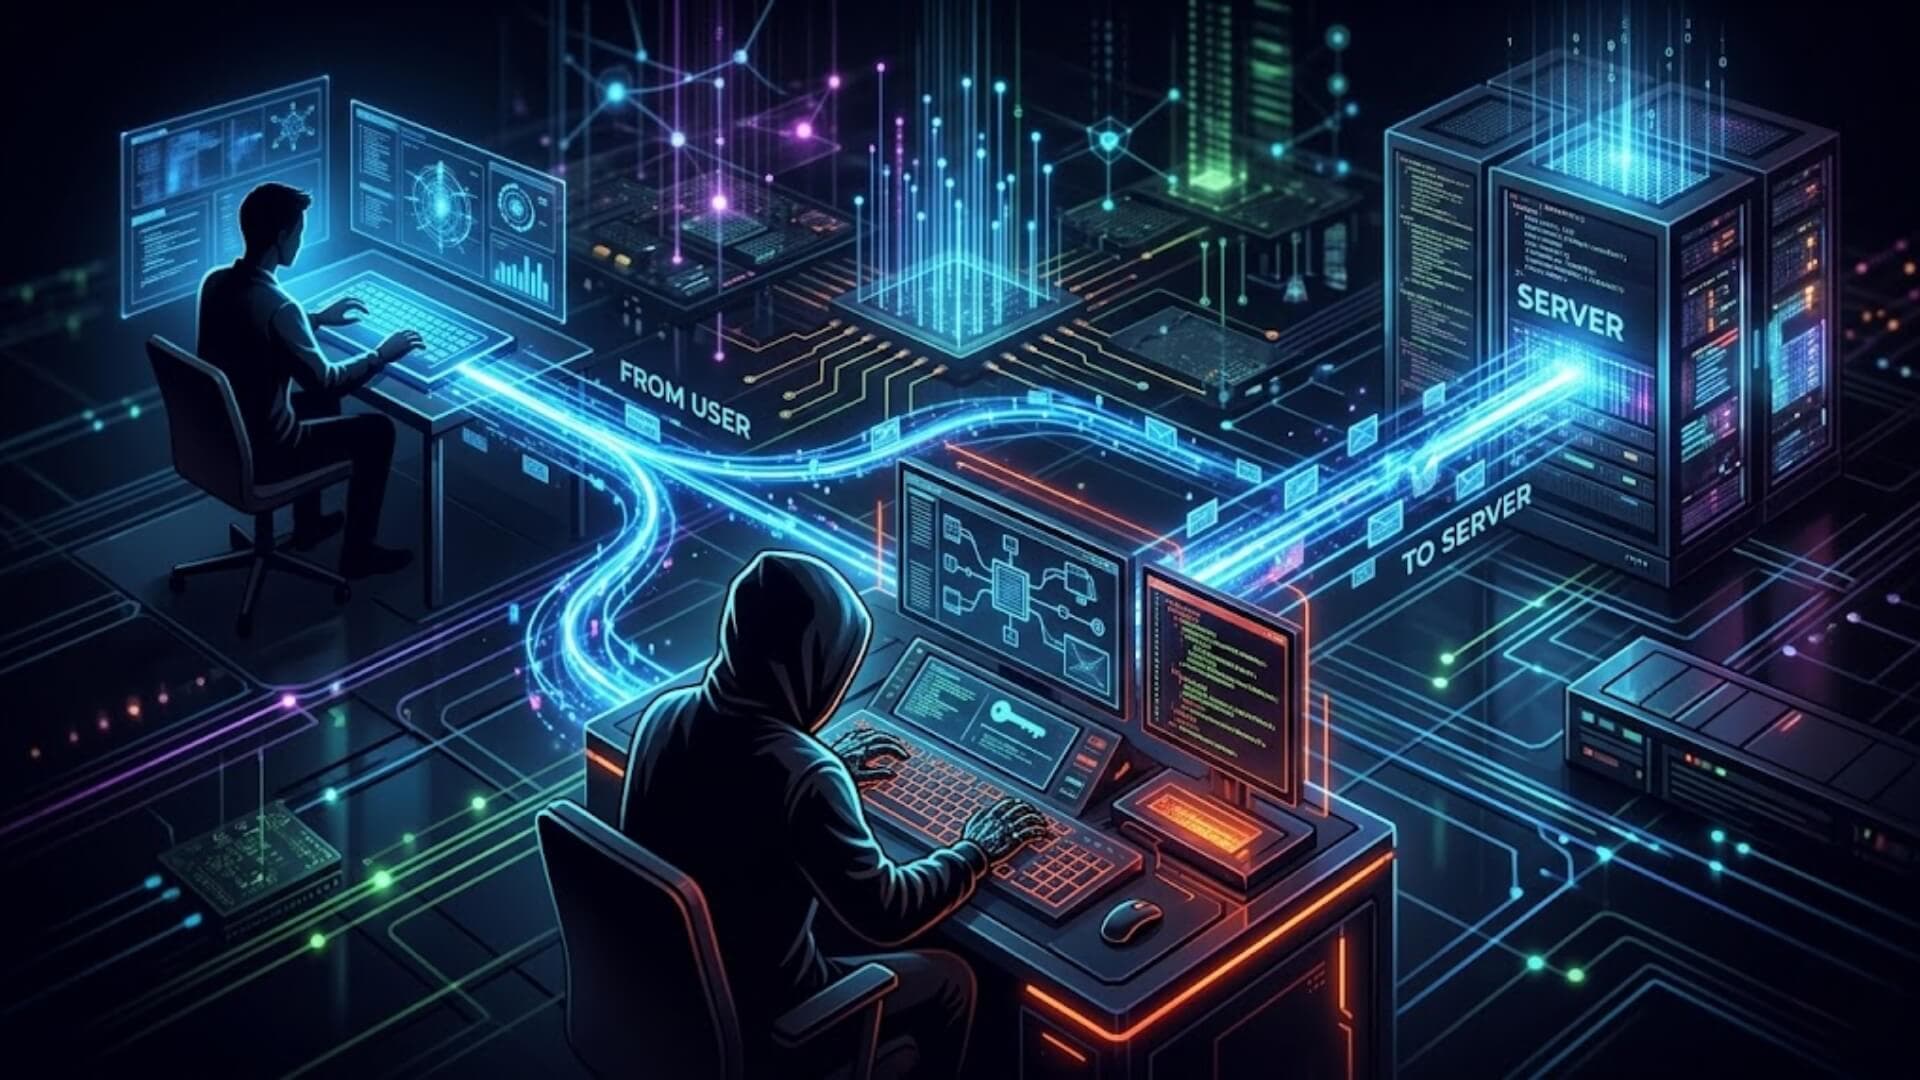
You're sitting at a coffee shop, connected to the free Wi-Fi, checking your bank account or logging into your work email. Everything looks normal. But somewhere between your laptop and the server, a hacker is quietly reading every byte of data you send: your passwords, your messages, your session tokens. You'd never know it happened.
This is exactly how a man in the middle attack works. It's one of the most dangerous yet least visible threats in cybersecurity today, and it doesn't just target large corporations. Anyone on an unsecured network is a potential victim.
In this guide, you'll learn what a man in the middle attack is, how attackers pull it off step by step, and 7 concrete ways to protect yourself and your organization before it's too late.
What is a Man in the Middle attack?Link to heading

A Man-in-the-Middle (MitM) attack is a type of cyberattack in which an attacker secretly inserts themselves between two parties that are actively communicating, typically between a web browser and a web server. Once positioned in the middle, the attacker intercepts the connection, impersonates one or both parties, and silently steals sensitive data without either side realizing what is happening.
MitM attacks are not limited to websites. They can occur across email communications, public Wi-Fi networks, and DNS lookups. E-commerce businesses and users of financial applications are among the most frequently targeted, since these environments involve the constant exchange of high-value credentials and payment data.
In most cases, neither the organization nor the individual user is aware that their connection has been compromised. This makes the consequences especially severe. Attackers can expose critical information such as usernames, passwords, and credit card numbers. They can also alter the content of communications in transit, which is particularly dangerous in financial transactions where even a small change can redirect funds or falsify records.
In more advanced cases, a successful MitM attack can give the attacker full control over an entire system.
>>> Learn more: What is an SSL port? Default ports, setup & troubleshooting
How does a Man in the Middle attack happen?Link to heading
MitM attacks fall into two primary categories. The first is physical MitM, where the attacker must be in close proximity to the victim's network or device. A common example is plugging a rogue router into a public wireless network or creating a fake access point to trick nearby users into connecting to it.
The second is software-based MitM, where the attacker deploys malware onto the victim's machine to intercept and manipulate access remotely. Keyloggers are a typical example, recording every keystroke typed on the infected device.
Regardless of the method used, MitM attacks generally unfold in two distinct phases: interception and decryption.
During the interception phase, the attacker captures all or part of the data being transmitted between two devices or servers. This is carried out using a range of techniques including ARP Spoofing, DNS Spoofing, and SSL Stripping, each of which exploits a different layer of the communication process.
During the decryption phase, the attacker processes the captured data to extract readable content. Encrypted information is broken down through various methods such as password cracking tools or by exploiting known security vulnerabilities in the encryption implementation itself.
Common forms of Man-in-the-Middle attacksLink to heading

MitM attacks come in several distinct forms, each targeting a different layer of communication. Below are the most widely used techniques that attackers rely on today.
IP SpoofingLink to heading
IP Spoofing involves the attacker forging the victim's IP address and using it to communicate with the other party as if they were the legitimate sender. With this position established, the attacker gains full access to all data being exchanged between the two parties without either side detecting the substitution.
DNS SpoofingLink to heading
DNS Spoofing works by manipulating DNS server records to redirect a domain name to a fraudulent website. When the victim types in a legitimate address, they are silently sent to a fake version of that site. Attackers use this technique either to artificially inflate traffic to a malicious site or to harvest login credentials entered by unsuspecting users.
HTTPS SpoofingLink to heading
HTTPS Spoofing exploits the trust users place in the padlock icon. The attacker creates a counterfeit HTTPS connection that appears secure on the surface, but the underlying connection is not properly encrypted. While the victim browses and interacts with what they believe is a trusted site, the attacker monitors every action and collects any information submitted.
SSL HijackingLink to heading
SSL Hijacking occurs when the attacker intercepts an SSL connection between a client and a server before it is fully established. By inserting themselves into this handshake process, they are able to re-encrypt the traffic on their own terms, giving them undetected access to the data flowing through the session.
Email HijackingLink to heading
Email Hijacking targets organizational email accounts, with financial institutions being a particularly common victim. Once the attacker has compromised or spoofed an account, they send messages to clients or partners that appear entirely legitimate, manipulating recipients into disclosing sensitive information or authorizing fraudulent transactions.
Wi-Fi EavesdroppingLink to heading
Wi-Fi Eavesdropping relies on setting up a rogue wireless access point in a public location, designed to mimic a legitimate network. Users who connect to it unknowingly route all their traffic through the attacker's infrastructure. This form of attack is especially prevalent at locations offering free public Wi-Fi, where users rarely scrutinize the network they are joining.
Browser Cookie TheftLink to heading
Browser Cookie Theft targets the session data stored within a user's browser cookies. These cookies often contain active authentication tokens that allow the attacker to access the victim's accounts directly, bypassing the need for a password entirely. Beyond account takeover, stolen cookies can also expose other personally identifiable information stored within active sessions.
How to Detect a Man in the Middle attackLink to heading

Most people only discover they were targeted after the damage is done. The good news is that a man in the middle attack does leave traces if you know what to look for. Recognizing the early warning signs and using the right detection tools can make the difference between catching an intrusion in time and suffering a full data breach.
Warning signs your connection may be compromisedLink to heading
The following signs do not automatically confirm an attack, but any one of them warrants immediate attention.
Your browser displays unexpected SSL certificate warnings or prompts you to accept a certificate from an unfamiliar issuer. This is one of the clearest red flags, as attackers often substitute their own certificates during an HTTPS spoofing attempt.
You notice that pages are loading slower than usual without any obvious reason. When a third party is intercepting and re-routing your traffic, the added processing introduces latency that is difficult to explain otherwise.
You are unexpectedly logged out of accounts or prompted to re-authenticate on platforms you were already signed into. This can indicate that your session token has been stolen and reused elsewhere.
Your network connection drops and reconnects repeatedly, especially on a public Wi-Fi network. This behavior is common when a rogue access point is competing with a legitimate one nearby.
You receive emails or messages that appear to come from a trusted contact but contain requests that seem unusual, out of context, or financially motivated. This is a strong indicator of email hijacking at the organizational level.
Tools to detect MITM attacksLink to heading
Beyond watching for warning signs manually, several tools are purpose-built to identify suspicious activity at the network level.
Wireshark is one of the most widely used network protocol analyzers available. It captures and displays traffic flowing through your network interface in real time, allowing you to inspect packets for anomalies such as unexpected ARP replies, duplicate IP addresses, or unrecognized certificate issuers.
XArp is a dedicated ARP attack detection tool that monitors ARP traffic on your local network. Since ARP Spoofing is one of the most common entry points for a man in the middle attack, XArp provides an accessible first line of defense for users who want targeted protection without analyzing raw packet data.
MitMf and Bettercap are tools originally designed for penetration testing but are also used by security teams to simulate and detect MitM conditions within their own infrastructure. Running controlled tests with these tools helps identify weaknesses before a real attacker finds them.
For organizations with dedicated IT teams, deploying an Intrusion Detection System such as Snort or Suricata provides continuous, automated monitoring of network traffic against known attack signatures, including patterns consistent with interception and session hijacking attempts.
How to prevent Man in the Middle attacks: 7 proven methodsLink to heading

Detection matters, but prevention is always the stronger position. The methods below address MitM attacks at multiple levels, from individual user habits to organization-wide technical controls. Implementing all seven significantly reduces your attack surface.
Use a VPN and know its limitationsLink to heading
A VPN encrypts the traffic between your device and the VPN server, making it considerably harder for an attacker on the same network to intercept readable data. This is especially valuable when connecting to public Wi-Fi, where Wi-Fi eavesdropping attacks are most common.
However, a VPN is not a complete solution on its own. It does not protect you from attacks that occur beyond the VPN endpoint, and a poorly configured or untrustworthy VPN provider can introduce new risks. Always choose a reputable provider with a verified no-logs policy and combine VPN use with the other methods listed below.
Always verify HTTPS and SSL certificatesLink to heading
Before submitting any sensitive information on a website, confirm that the connection is using HTTPS and that the SSL certificate is valid and issued by a trusted certificate authority. Click on the padlock icon in your browser's address bar and review the certificate details, paying attention to the issuing organization and expiration date.
Be cautious of any browser warning about certificate mismatches or untrusted issuers. These warnings exist precisely to alert you when something in the certificate chain does not add up, which is a common outcome of HTTPS spoofing and SSL hijacking.
Enable HSTS and certificate pinningLink to heading
HTTP Strict Transport Security (HSTS) is a web security policy that instructs browsers to only communicate with a server over HTTPS, preventing any downgrade to an unencrypted HTTP connection. For website owners and developers, enabling HSTS on your server is one of the most effective technical controls against SSL Stripping attacks.
Certificate Pinning goes a step further by associating a specific public key with a given server, so that any attempt to substitute a different certificate is automatically rejected by the client. This is particularly relevant for mobile applications and enterprise systems that communicate with known, fixed endpoints.
Use strong multi-factor authenticationLink to heading
Multi-factor authentication adds a second verification layer that an attacker cannot bypass simply by stealing your password. Even if a man in the middle attack successfully captures your login credentials, MFA ensures that credential alone is not enough to gain access to your account.
Use authenticator apps rather than SMS-based verification wherever possible, since SIM swapping attacks can compromise text message delivery. For high-value systems, hardware security keys such as YubiKey provide the strongest available protection against credential-based attacks.
Avoid unsecured public Wi-Fi networksLink to heading
Public Wi-Fi networks are the most common environment for man in the middle attacks, particularly Wi-Fi eavesdropping and rogue access point attacks. If a network requires no password, offers an unusually generic name, or appears as a duplicate of a known network nearby, treat it as potentially hostile.
When using public Wi-Fi is unavoidable, connect through a VPN immediately, avoid accessing banking or sensitive accounts, and never approve unexpected certificate warnings that appear during the session.
Keep software, browsers and certificates updatedLink to heading

A significant portion of successful MitM attacks exploit known vulnerabilities in outdated software. Browser updates frequently include patches for flaws in how TLS certificates are validated. Operating system updates address weaknesses in network stacks. Certificate authority updates ensure your device trusts only legitimate issuers.
Enable automatic updates across all devices and applications, and pay particular attention to the expiration dates of any SSL certificates your organization manages. An expired or misconfigured certificate not only creates security exposure but also erodes user trust at the moment it matters most.
Use End-to-End Encrypted communication toolsLink to heading
End-to-end encryption ensures that only the sender and the intended recipient can read the contents of a message. Even if an attacker successfully intercepts the transmission, the data they capture is cryptographically unreadable without the private keys held exclusively by the two parties.
For team communication, platforms such as Signal offer robust end-to-end encryption by default. For business email, consider implementing S/MIME or PGP encryption on sensitive correspondence. For file transfers and API communication, ensure that TLS 1.2 or higher is enforced at every endpoint and that weak cipher suites are explicitly disabled in your server configuration.
ConclusionLink to heading
A man in the middle attack can turn an ordinary online session into a serious security risk in just moments. That is why basic protection is never enough on its own.
The best defense is a layered one. Strong HTTPS enforcement, updated browsers, secure authentication, VPN use on risky networks, and careful attention to certificate warnings all help reduce the chance of interception. By taking these steps seriously, users and businesses can make it much harder for a man in the middle attack to succeed.
>>> Can your WordPress website detect malicious access attempts before it is too late? Activate W7SFW today to stop dangerous attacks before they escalate.